
Company Super Admin App
Company setup, delegated rights and business-wide oversight.
View application purpose →Application release pending In development
Turn recovery-download security events into reviewed incidents, assigned department responses and independent manager decisions.
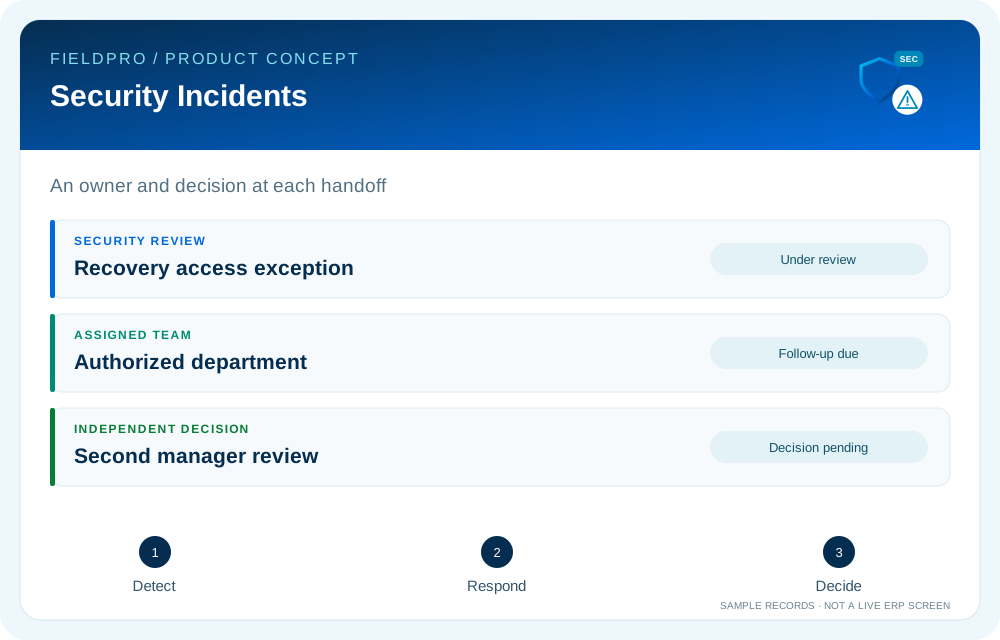
Company-scoped recent events and failure counters cover recovery grant creation, redemption and integrity failures without exposing tokens or file paths.
Open a review for a company user and require another reviewer to close it. The source also provides temporary manual recovery-download restrictions.
Escalate an open review to an incident. The opener cannot acknowledge or resolve their own incident; the independent acknowledging admin records the resolution.
Company policy controls acknowledgment and resolution targets. Assignment validates active company and department membership.
A scheduled worker routes overdue assigned incidents through configured active department members at levels 1–5. It records internal notices and dispatch history.
A designated recipient records one response note per dispatch. An escalation response is distinct from resolving the incident.
Per-level response targets, overdue response alerts and bounded 30-day department performance reports are present in source.
Formal active department managers receive follow-ups. A different authorized manager decides approval or rejection before permitted closure.
Reopen an eligible rejected review with a reason, preserve prior decisions and resubmit for independent review.
The manager dashboard exposes permitted review, follow-up, decision, close, rework, notice-read and export controls.
New decision/rework actions write chained audit entries; tenant-scoped CSV neutralizes spreadsheet formulas. The chain is not externally anchored and cannot defeat a privileged database rewrite.
Company setup, delegated rights and business-wide oversight.
View application purpose →Application release pendingCoordinate branch operations, assigned supervisors and exceptions within delegated rights.
View application purpose →Application release pending
Review assigned team progress and raise operational issues with the responsible department.
View application purpose →Application release pending
Assigned support tickets, assets and approved assistance responsibilities.
View application purpose →Application release pendingModule access follows assigned rights. Application package releases and live connections are separate.
Source present · live validation pending. Release availability requires the relevant implementation, integration and validation work. The visual above is illustrative.
Explore the departments and handoffs that match your operation, then prepare a product enquiry around your company structure.